The Evolving Cybersecurity Threat Landscape: Protecting Critical Infrastructure
In an increasingly interconnected world, the stability and functionality of nations hinge significantly on the resilience of their critical infrastructure. From power grids and water treatment plants to transportation networks and financial systems, these essential services are the backbone of modern society. However, this reliance on digital systems has also exposed them to a burgeoning and sophisticated threat: cyberattacks. The cybersecurity critical infrastructure landscape is not merely evolving; it is transforming at an unprecedented pace, presenting challenges that demand continuous vigilance and innovative solutions.
The past decade has witnessed a dramatic escalation in the frequency, sophistication, and impact of cyberattacks targeting critical infrastructure. What were once theoretical risks have materialized into tangible threats, capable of causing widespread disruption, economic damage, and even loss of life. Government agencies, industry leaders, and cybersecurity experts worldwide are grappling with the urgent need to fortify defenses and develop proactive strategies to protect these vital assets. This article delves into the complexities of the current cybersecurity critical infrastructure threat landscape, explores the motivations behind these attacks, and outlines comprehensive strategies for robust protection.
Understanding the Escalating Threat to Cybersecurity Critical Infrastructure
The notion of a ‘cyber Pearl Harbor’ might have once seemed like hyperbole, but the reality of nation-state sponsored attacks, sophisticated criminal enterprises, and even ideologically motivated groups targeting critical infrastructure has brought this concept into sharper focus. The motives behind these attacks are diverse, ranging from espionage and intellectual property theft to political destabilization and financial gain. Regardless of the intent, the consequences can be catastrophic.
Recent reports indicate a significant uptick in cyberattacks against critical infrastructure sectors. For instance, the US Department of Homeland Security reported a substantial increase in incidents targeting energy and manufacturing sectors in the last year alone. This surge isn’t just about volume; it’s about the increasing complexity and adaptability of the adversaries. Attackers are leveraging advanced persistent threats (APTs), zero-day exploits, and highly customized malware designed to evade traditional security measures. The shift towards operational technology (OT) and industrial control systems (ICS) being connected to enterprise networks has created new attack vectors, blurring the lines between IT and OT security and complicating defense strategies for cybersecurity critical infrastructure.
Advertisement
One of the primary challenges in securing cybersecurity critical infrastructure is the inherent legacy nature of many of these systems. Designed decades ago, often with little to no consideration for cybersecurity, these systems are difficult and expensive to upgrade. Patching vulnerabilities can disrupt operations, leading to a Catch-22 situation where security improvements are deferred due to operational concerns. Furthermore, the specialized nature of OT/ICS environments means that traditional IT security tools and personnel often lack the necessary expertise to effectively monitor and defend them.
Key Vulnerabilities and Attack Vectors
To effectively protect cybersecurity critical infrastructure, it is crucial to understand the common vulnerabilities and attack vectors exploited by malicious actors:
- Legacy Systems and Outdated Software: Many critical infrastructure components rely on aged hardware and software that are no longer supported by vendors, making them susceptible to known vulnerabilities.
- Insider Threats: Disgruntled employees or individuals coerced by external actors can provide access to sensitive systems, bypassing perimeter defenses.
- Supply Chain Attacks: Compromising a less secure vendor or supplier in the supply chain can provide a backdoor into a critical infrastructure organization. The SolarWinds attack serves as a stark reminder of this vector’s potency.
- Phishing and Social Engineering: Human error remains a significant vulnerability. Cleverly crafted phishing emails can trick employees into revealing credentials or installing malware.
- Lack of Segmentation: Insufficient network segmentation allows attackers, once inside, to move laterally across systems and gain access to critical operational technology.
- Inadequate Patch Management: Delays in applying security patches leave systems exposed to well-known exploits.
- Internet of Things (IoT) Vulnerabilities: The proliferation of IoT devices within critical infrastructure environments introduces new entry points that may not be adequately secured or monitored.
The convergence of IT and OT networks, while offering benefits in terms of efficiency and data analytics, has also expanded the attack surface. An attack originating in the IT domain can now potentially pivot into the OT domain, directly impacting physical operations. This interdependency necessitates a holistic approach to cybersecurity critical infrastructure that considers both IT and OT security as equally vital.
Advertisement
Strategies for Robust Cybersecurity Critical Infrastructure Protection
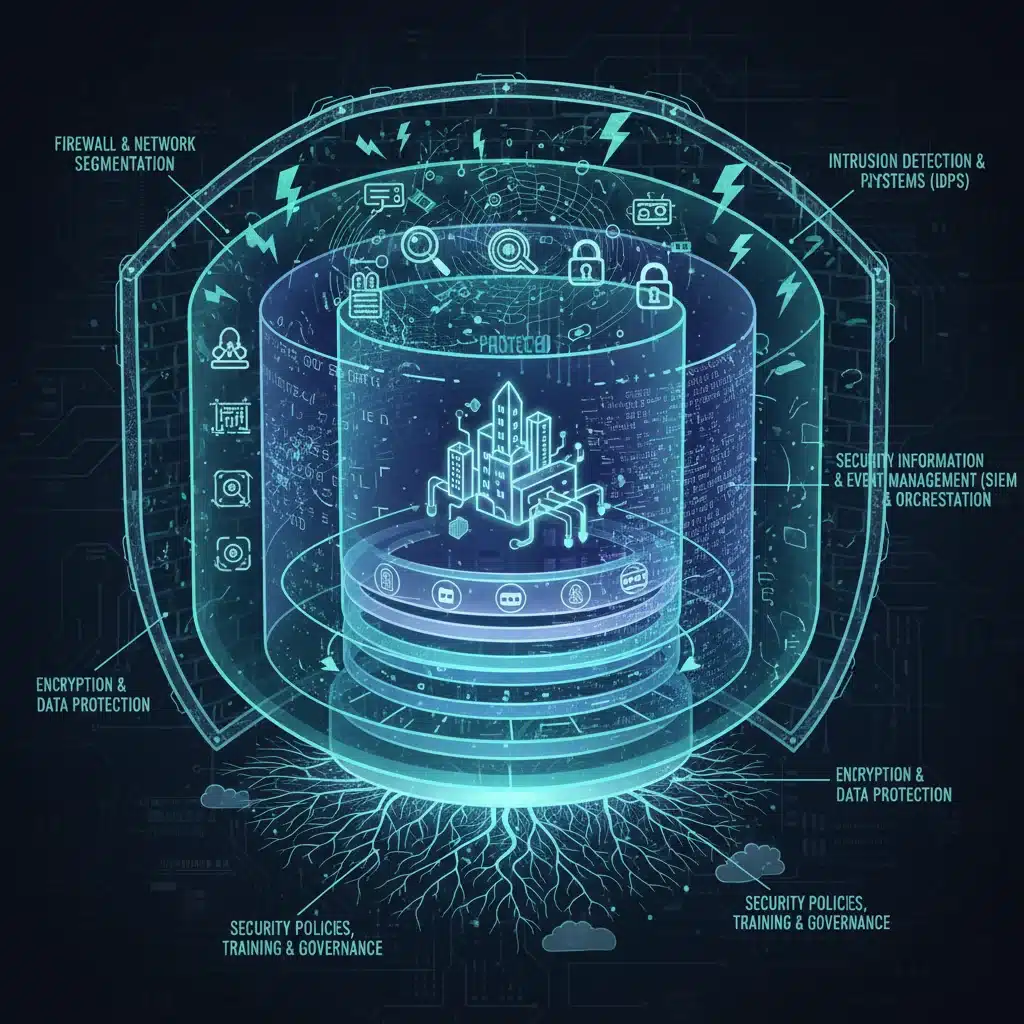
Protecting critical infrastructure requires a multi-faceted, layered approach that encompasses technology, policy, people, and processes. No single solution can provide complete immunity, but a comprehensive strategy can significantly enhance resilience and reduce the likelihood and impact of successful attacks.
1. Comprehensive Risk Assessment and Management
The first step in any effective security strategy for cybersecurity critical infrastructure is a thorough understanding of the assets, threats, and vulnerabilities. This involves:
- Asset Inventory: Identifying all critical assets, both IT and OT, and their interdependencies.
- Threat Modeling: Anticipating potential attack scenarios and understanding adversary capabilities and motivations.
- Vulnerability Assessments and Penetration Testing: Regularly testing systems to identify weaknesses before attackers do.
- Risk Prioritization: Focusing resources on protecting the most critical assets from the most probable and impactful threats.
Risk management should be an ongoing process, adapting to new threats and changes in the operational environment. It’s not a one-time exercise but a continuous cycle of identification, assessment, mitigation, and monitoring.
3. Enhancing Operational Technology (OT) Security
Securing OT environments requires specialized knowledge and tools. Strategies include:
- OT-Specific Monitoring and Detection: Deploying intrusion detection systems (IDS) and security information and event management (SIEM) solutions tailored for industrial protocols and behaviors.
- Network Segmentation and Air Gapping: Physically or logically separating OT networks from IT networks where feasible, or implementing robust firewalls and unidirectional gateways.
- Secure Remote Access: Ensuring all remote access to OT systems is heavily authenticated, encrypted, and monitored.
- Endpoint Protection for OT: Implementing specialized endpoint detection and response (EDR) solutions that can operate within the constraints of OT systems.
4. Robust Incident Response and Recovery Planning
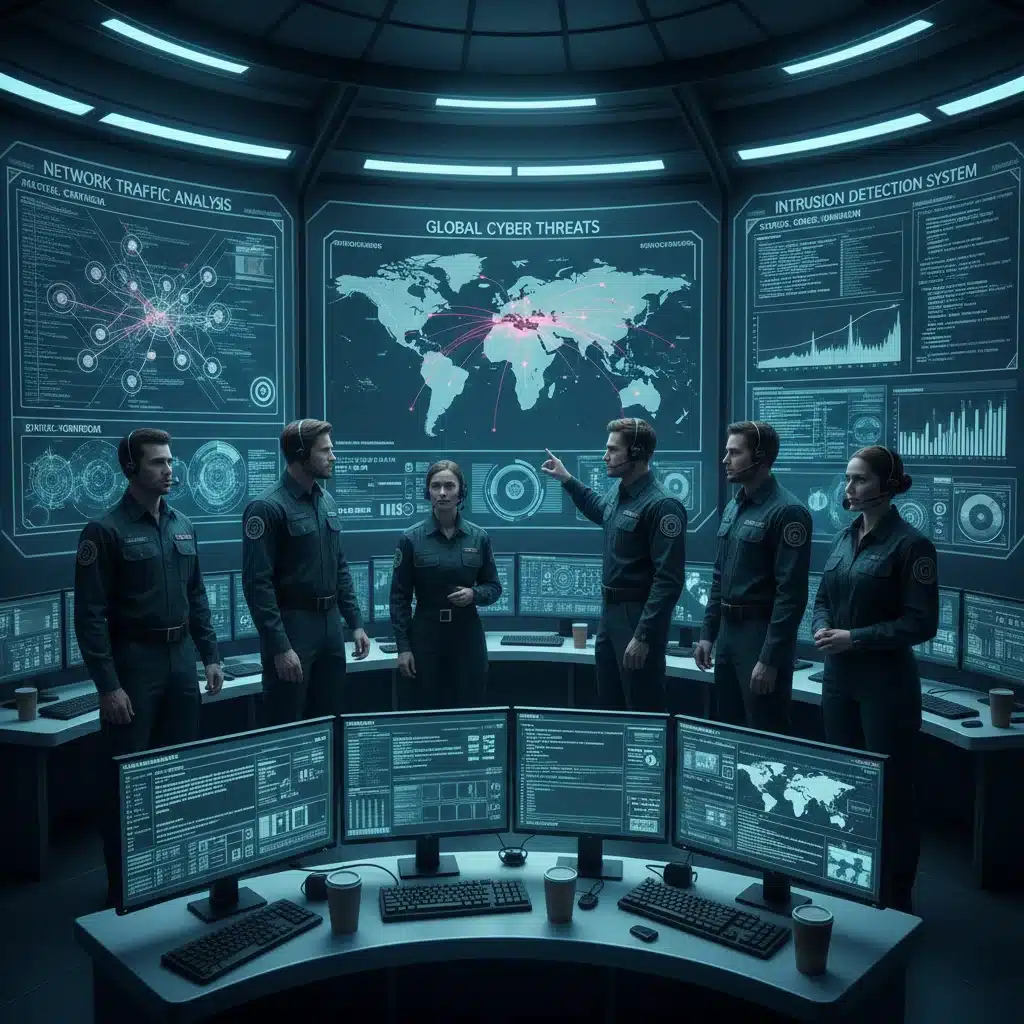
Even with the best defenses, a breach is always a possibility. A well-defined and regularly tested incident response plan is critical for minimizing the impact of an attack on cybersecurity critical infrastructure. This plan should include:
- Detection and Analysis: Promptly identifying and understanding the scope of an incident.
- Containment: Limiting the spread and impact of the attack.
- Eradication: Removing the threat from the systems.
- Recovery: Restoring affected systems and data to normal operation.
- Post-Incident Review: Learning from the incident to improve future defenses.
Regular drills and simulations are essential to ensure that personnel are familiar with their roles and responsibilities during a crisis. The ability to quickly and effectively respond can be the difference between a minor disruption and a catastrophic failure.
5. Supply Chain Risk Management
As illustrated by numerous high-profile attacks, the supply chain is a significant vulnerability. Organizations must implement rigorous vetting processes for all third-party vendors and suppliers. This includes:
- Security Audits: Conducting regular security assessments of suppliers.
- Contractual Obligations: Ensuring suppliers adhere to strict cybersecurity requirements.
- Software Bill of Materials (SBOM): Requiring vendors to provide detailed lists of all components in their software to identify potential vulnerabilities.
- Monitoring and Threat Intelligence Sharing: Collaborating with suppliers to share threat intelligence and monitor for compromises.
6. Workforce Development and Training
Human capital is arguably the most critical asset and the most significant vulnerability in cybersecurity critical infrastructure. A skilled and aware workforce is indispensable:
- Cybersecurity Awareness Training: Regular training for all employees on identifying phishing attempts, safe browsing practices, and corporate security policies.
- Specialized OT Security Training: Providing in-depth training for IT and OT personnel on the unique challenges and solutions for securing industrial control systems.
- Talent Recruitment and Retention: Investing in programs to attract and retain cybersecurity professionals, given the global shortage of skilled personnel.
7. Regulatory Compliance and Collaboration
Adhering to industry-specific regulations and collaborating with government agencies and industry peers are crucial for strengthening cybersecurity critical infrastructure. Frameworks like the NIST Cybersecurity Framework, NERC CIP (for the electric sector), and various international standards provide guidelines for best practices.
Information sharing between government and private sectors, as well as among industry competitors, is vital for understanding emerging threats and developing collective defenses. Threat intelligence platforms and sector-specific information sharing and analysis centers (ISACs) play a critical role in disseminating timely warnings and mitigation strategies.
The Future of Cybersecurity Critical Infrastructure
The battle for cybersecurity critical infrastructure is a continuous one, with adversaries constantly evolving their tactics. Looking ahead, several trends will shape the future of protection efforts:
- Artificial Intelligence and Machine Learning: AI and ML will be increasingly deployed for advanced threat detection, anomaly identification, and automated response, helping to cope with the sheer volume and speed of modern attacks. However, these technologies also present new attack surfaces if not secured properly.
- Quantum Computing: The advent of quantum computing poses both a threat (potentially breaking current encryption standards) and an opportunity (for developing quantum-resistant cryptography). Organizations must begin preparing for a post-quantum cryptographic future.
- Increased Automation and Orchestration: Security operations will become more automated, allowing security teams to respond faster and more efficiently to incidents, freeing up human analysts for more complex tasks.
- International Cooperation: As cyberattacks transcend national borders, international collaboration, intelligence sharing, and joint defense exercises will become even more critical.
- Resilience Engineering: Beyond prevention, there will be a greater emphasis on designing systems that are inherently resilient, capable of operating even when parts of them are compromised. This involves redundancy, graceful degradation, and rapid recovery capabilities.
The integration of security by design principles from the very inception of new critical infrastructure projects will be paramount. Retrofitting security into existing systems is far more challenging and costly than building it in from the ground up.
Conclusion
The protection of cybersecurity critical infrastructure is not merely a technical challenge; it is a matter of national security, economic stability, and public safety. The evolving threat landscape demands a dynamic, proactive, and comprehensive approach that integrates advanced technology, robust policies, skilled personnel, and strong partnerships across government and industry.
Organizations responsible for critical infrastructure must move beyond compliance-driven security to a risk-based, adaptive security posture. Investing in cutting-edge security solutions, fostering a culture of cybersecurity awareness, and continuously refining incident response capabilities are no longer optional but imperative. By embracing these strategies, we can collectively build a more resilient and secure digital future, safeguarding the essential services that underpin our modern world from the persistent and sophisticated threats that seek to undermine them.
The journey to secure cybersecurity critical infrastructure is ongoing, requiring sustained effort and innovation. However, with a concerted and collaborative approach, we can significantly enhance our ability to detect, prevent, and respond to cyberattacks, ensuring the continuity and integrity of our most vital assets.